
Fraudulent voting on WhatsApp is spreading even among IT professionals. One code is enough and an attacker can take over the entire WhatsApp account
In recent days a phishing campaign aimed at WhatsApp users has been spreading significantly in the Czech Republic. The message arrives from a trusted contact and asks for a “vote in a contest” for a friend’s daughter. The link leads to a page that looks like a normal poll, but is actually part of a sophisticated account takeover mechanism.

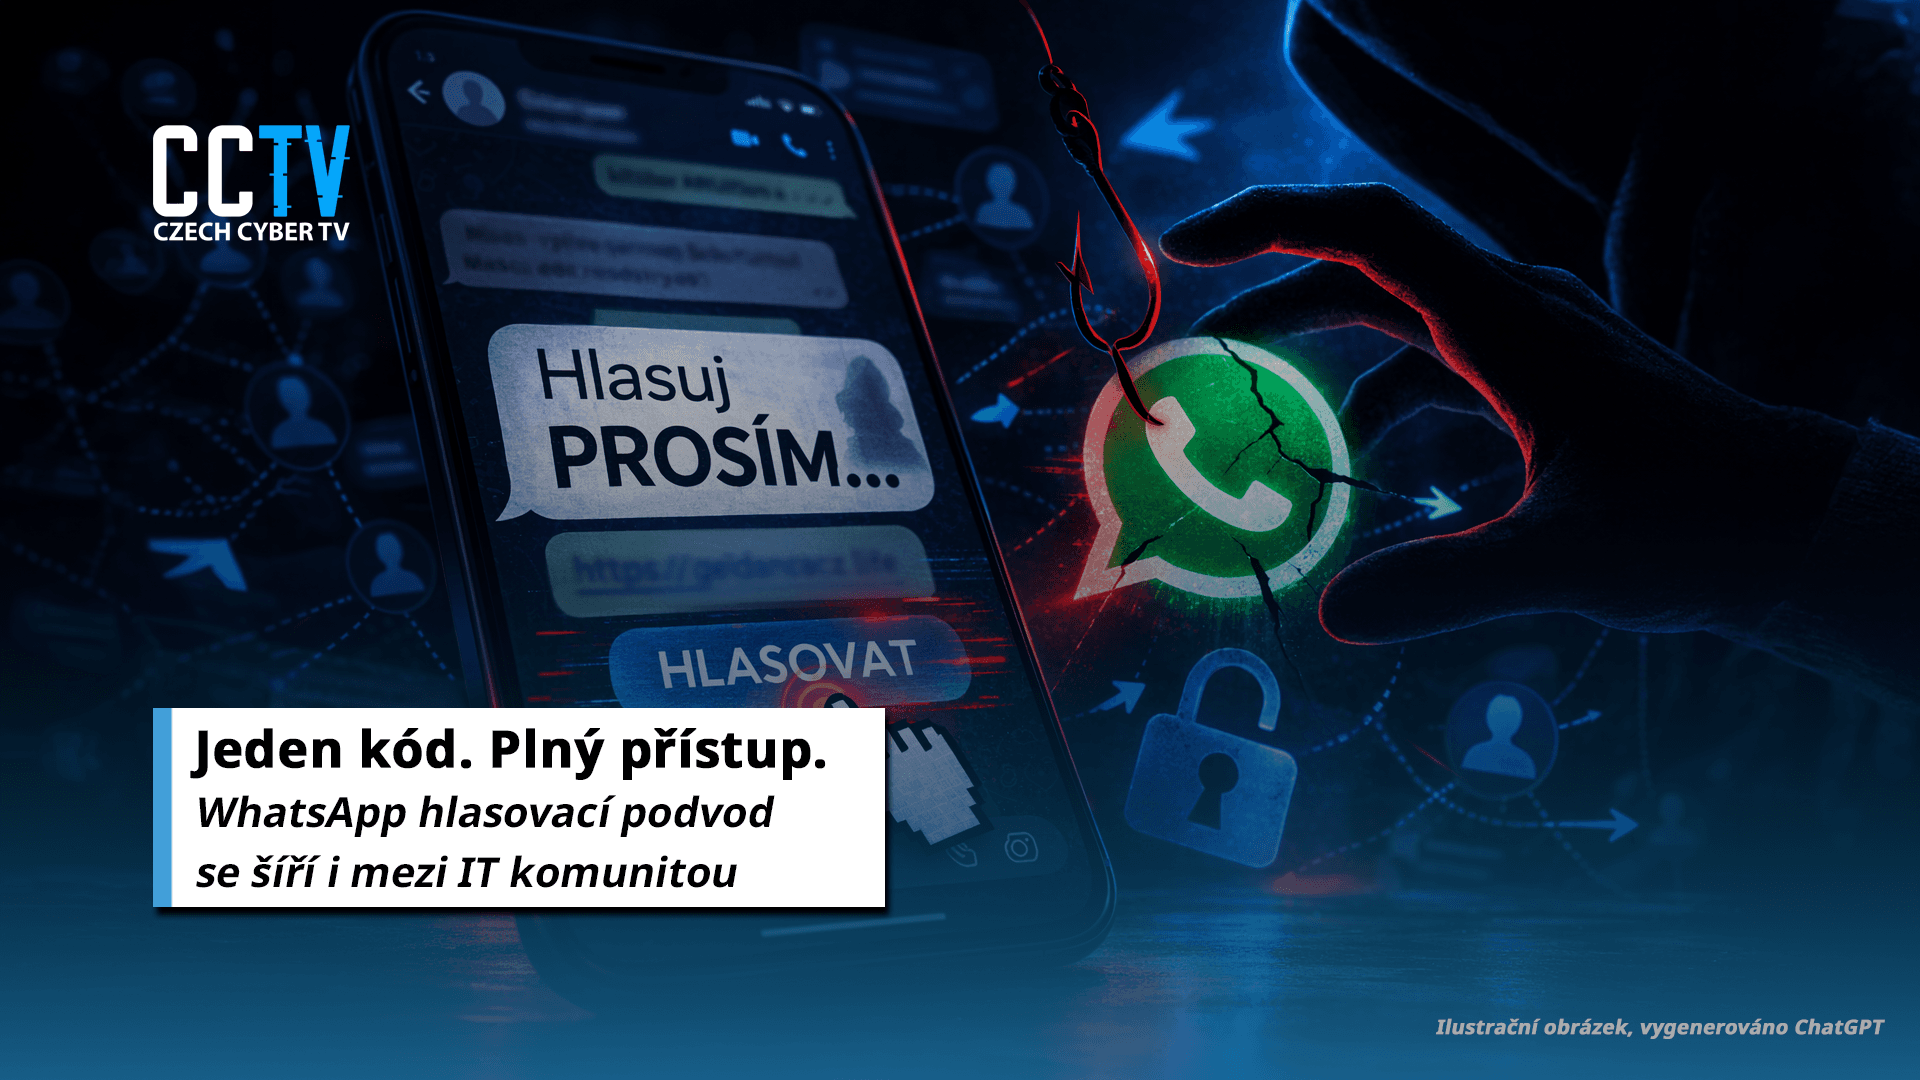
In recent days a phishing campaign aimed at WhatsApp users has been spreading significantly in the Czech Republic. The message arrives from a trusted contact and asks for a “vote in a contest” for a friend’s daughter. The link leads to a page that looks like a normal poll, but is actually part of a sophisticated account takeover mechanism.
The campaign is not new; in various variants it has appeared across Europe. Security companies and foreign media including BleepingComputer have previously warned that this type of attack targets the trust between known contacts and spreads chain-wise through compromised accounts.
Currently, however, based on experiences from the Czech scene, it is also affecting users in the IT and security community.
Jak podvod začíná
The attacker first compromises one WhatsApp account. They then send a message from it to all of the victim’s contacts. The text is usually very similar:
„Ahoj, můžeš prosím hlasovat pro Katarínu v této anketě? Je to dcera mé kamarádky. Hlavní výhrou je stipendium a je to pro ni moc důležité.“
The message contains a link to a domain that at first glance does not look explicitly suspicious, but usually uses generic or cheap TLDs (.life, .xyz, .top etc.). The website imitates a voting contest – it contains photos, a "Hlasovat" button and sometimes a fake vote counter.
Co se stane po kliknutí
Simply opening the page usually does not lead to malware installation. The core of the attack lies elsewhere.
- The user clicks on "Hlasovat".
- The page asks for a phone number, supposedly to verify the vote.
- A six-digit code from WhatsApp then arrives.
- The page asks to enter this code.
At this point the account takeover occurs.
The entered code is not a confirmation of the vote, but a verification of the login. Using this method the attacker pairs their browser or device as another logged-in instance of WhatsApp. They effectively gain access to the victim’s account.
This is not a technical exploit or a zero-day vulnerability. It is pure social engineering based on abusing trust and inattention.
Co útočník získá
After successful verification of the code the attacker can:
- read ongoing conversations,
- send messages on behalf of the victim,
- continue spreading the phishing campaign,
- and possibly move on to other frauds (for example requests for quick financial help).
This is why the campaign spreads so quickly. Each newly compromised account generates dozens of potential victims.
Trust plays a crucial role here. The message does not come from an anonymous sender, but from a known person – a colleague, friend or family member.
Proč funguje i na zkušené uživatele
The attack does not use sophisticated malware. It exploits human behavior.
- The request appears personal.
- The text evokes empathy.
- It does not contain obviously malicious attachments.
- It arrives within normal work or personal communication.
Especially busy people react quickly and automatically. That is precisely the strength of the campaign.
Co dělat, pokud jste zadali kód
If the user has already entered the verification code, it is necessary to act immediately.
- Open WhatsApp → Nastavení → Propojená zařízení.
- Log out of any unknown or suspicious devices.
- Enable dvoufázové ověření (PIN kód).
- Inform your contacts that the account may have been compromised.
In some cases attackers move faster. After taking over the account they may:
- activate their own dvoufázové ověření,
- change security settings,
- repeatedly attempt to log in so that the account becomes temporarily blocked.
Some victims have thus lost access to their account completely. In such a situation it is no longer possible to simply "log out" a device from the app because the victim cannot access it.
The only option is to start the account recovery process directly through WhatsApp's official support and verify ownership of the phone number. This process can take several days and during that time the attacker may continue to misuse the account.
If financial damage has occurred, you should immediately contact your bank and Policie ČR.
Jak se bránit do budoucna
The basic rules are simple:
- Never enter a verification code from SMS into a website.
- Verify any request to "vote" via another communication channel.
- Regularly check connected devices in the app.
- Keep dvoufázové ověření active.
It is also important to remind that simply clicking on the link usually does not mean compromise. The critical moment is entering the verification code.
Řetězová reakce důvěry
This type of campaign is an example of a modern „chain trust“ attack. The attacker does not need to convince thousands of people directly. It is enough to compromise a few accounts and the trust between contacts will do the rest.
At a time when users are accustomed to technical attacks and malware, paradoxically the greatest risk may be a simple, personal request.